Overview
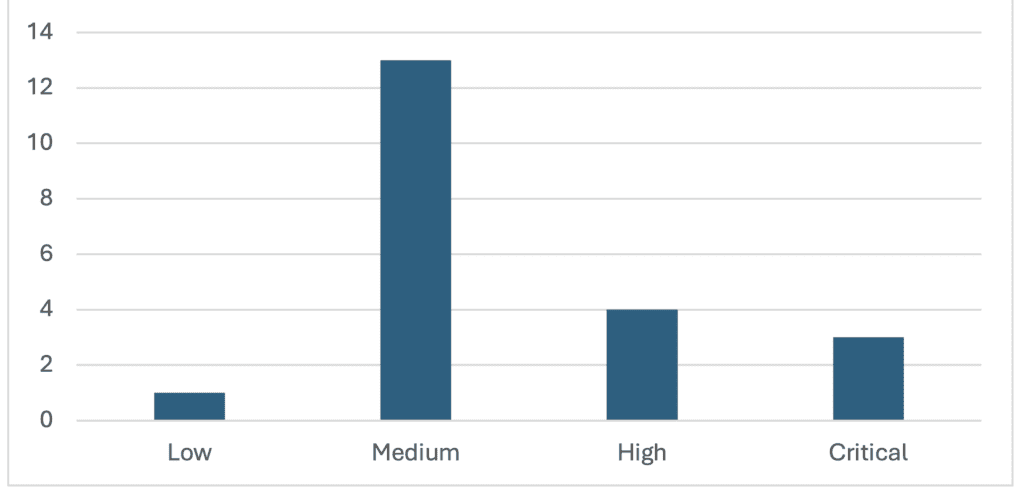
SAP’s security patch day for October 2026 has seen the release of 21 OSS SAP security notes. Three notes have been classified as critical, four as high, 13 as medium and one as low based on the CVSS v3.0 Rating.
Security Notes by CVSS v3 Base Score
Four notes have been released for:
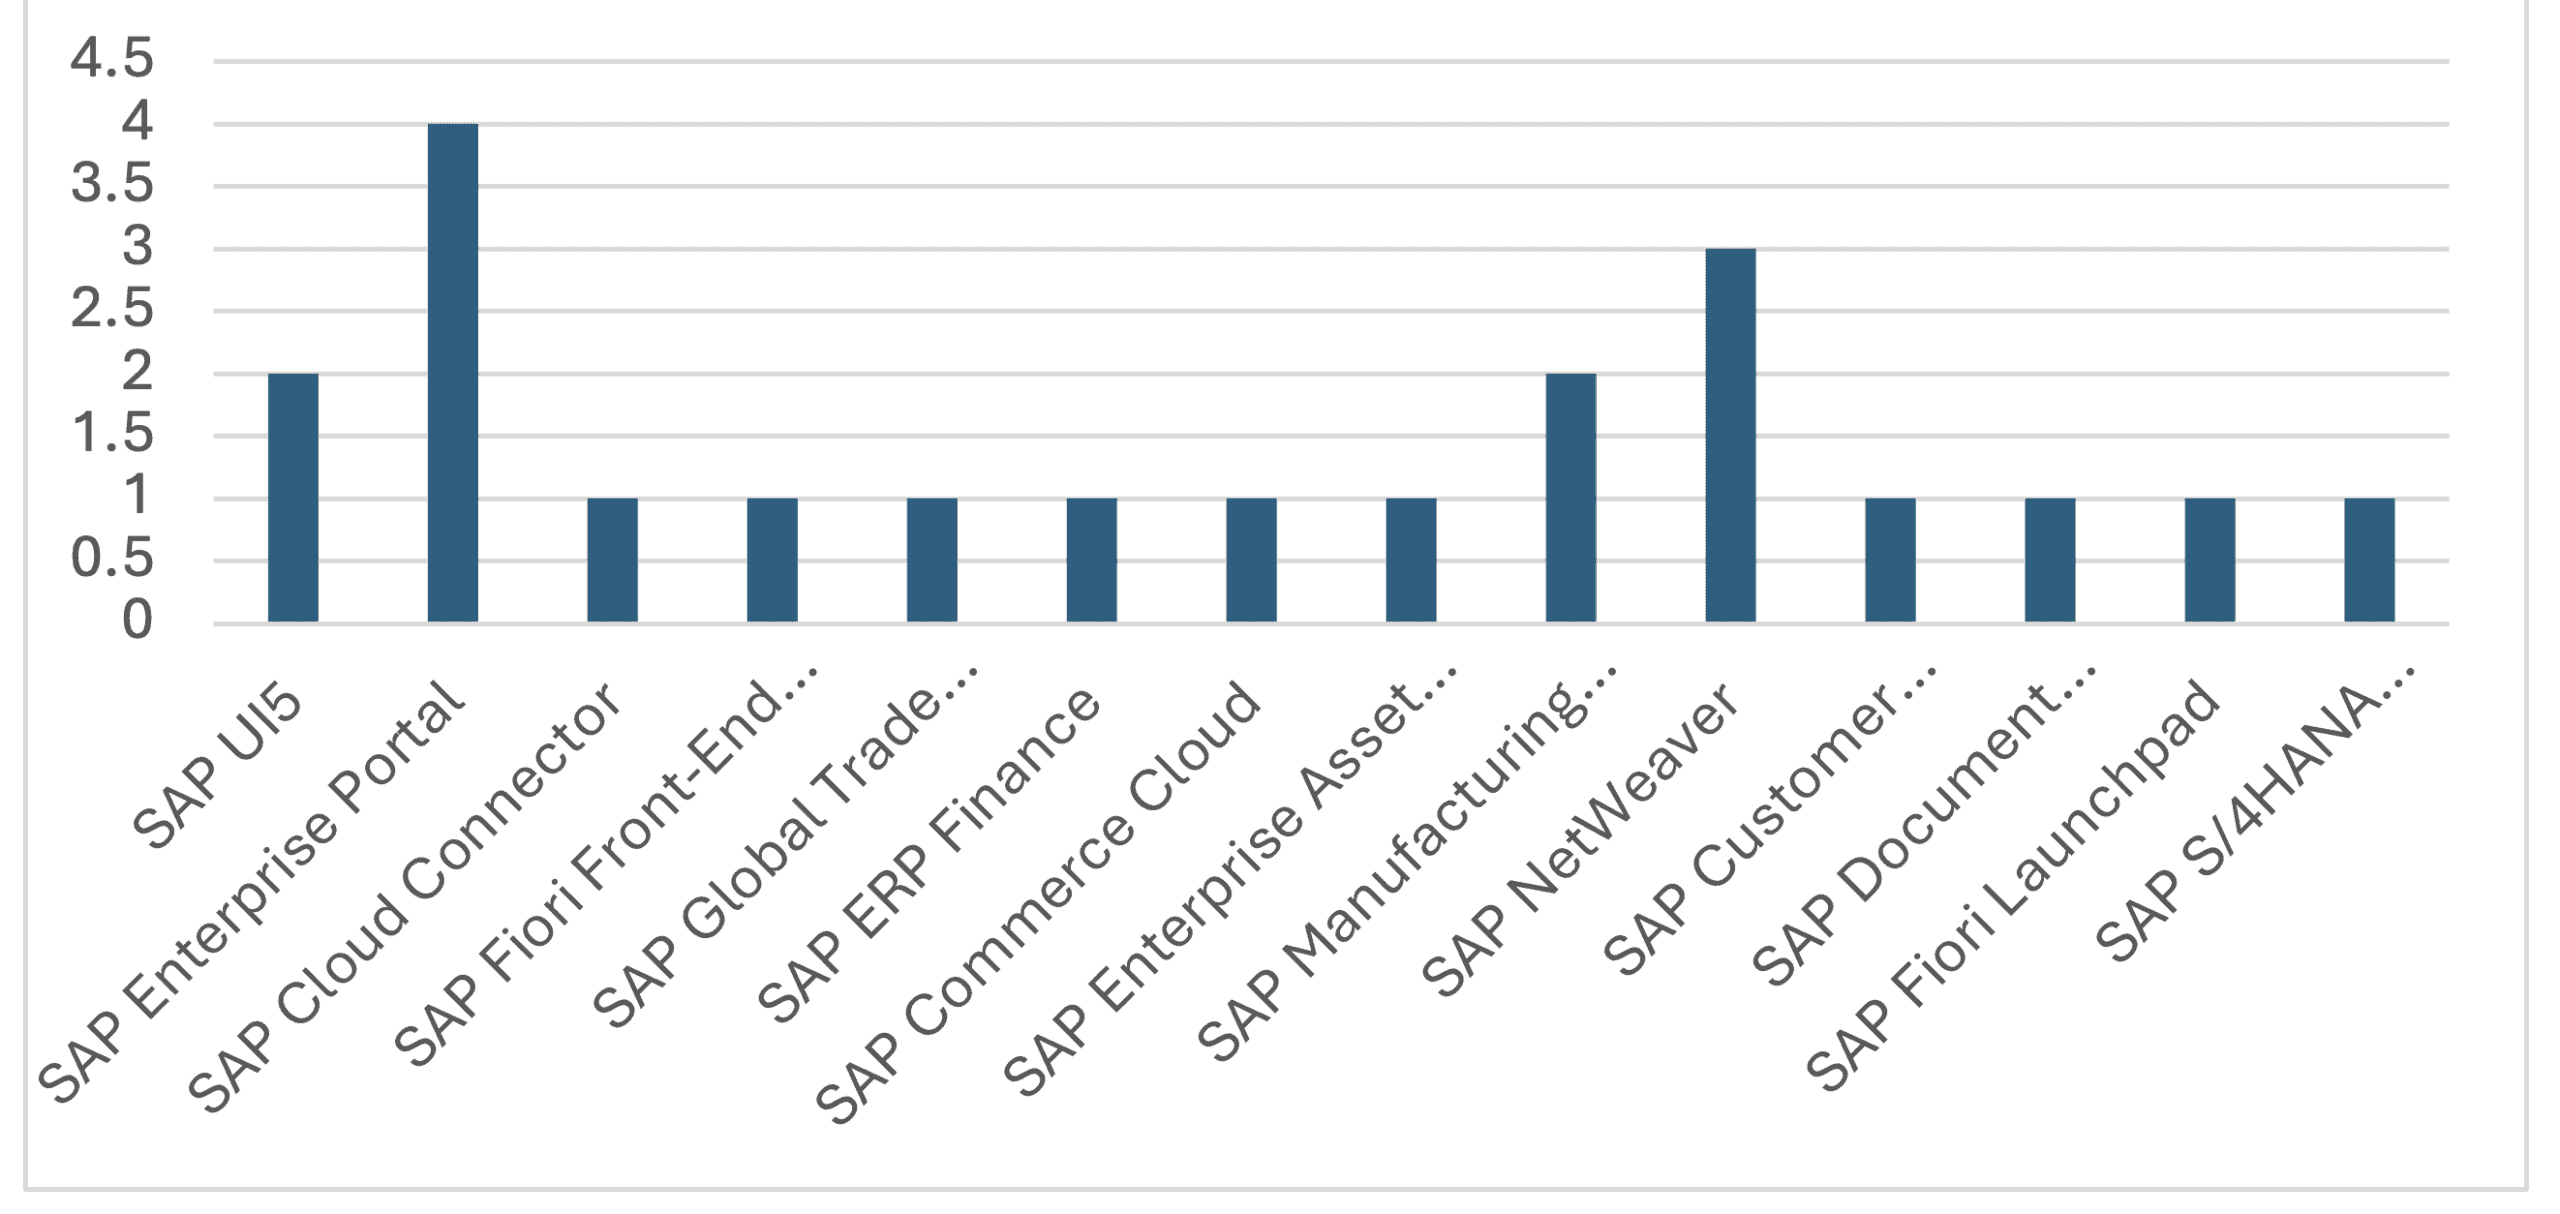
- SAP Enterprise Portal
Three notes have been released for:
- SAP NetWeaver
Two notes have been released for:
- SAP Manufacturing Integration and Intelligence
- SAP UI5
Single notes have been released for:
- SAP Cloud Connector
- SAP Fiori Front-End Server
- SAP Global Trade Services
- SAP ERP Finance
- SAP Commerce Cloud
- SAP Enterprise Asset Management
- SAP Customer Relationship Management
- SAP Document Management System
- SAP Fiori Launchpad
- SAP S/4HANA Advanced ATP
Security Notes by Product Category
Vulnerabilities: October 2026 Highlights
[CVE-2026-89107] Code Injection vulnerability in SAP S/4HANA (Manage Substitution/Validation Rules) (SAP Note 3805589)
SAP S/4HANA (Manage Substitution/Validation Rules) does not sufficiently validate input processed by rule definition functionality that utilizes a domain-specific scripting language. An authenticated attacker with specific business privileges could submit specially crafted input, which is interpreted as executable ABAP code by the rule processing logic. Successful exploitation could allow the attacker to execute ABAP arbitrary code into the system, resulting in full compromise of the affected system and high impact on confidentiality, integrity, and availability of the system.
[CVE-2026-58249 ] Memory Corruption vulnerability in SAP NetWeaver and SAP Web Dispatcher (Internet Communication Manager) (SAP Note 3765424)
SAP NetWeaver and SAP Web Dispatcher do not properly validate certain fields in specially crafted requests handled by an internal protocol component. An unauthenticated attacker could send a malicious request that triggers a memory-handling error, causing the affected process to crash. Successful exploitation can therefore result in a high impact on the availability of the affected application. There is no impact on the confidentiality or integrity of the application.
[CVE-2026-66766] Denial of Service (DoS) due to use of third-party component in SAP S/4HANA (Manage Supply Protection) (SAP Note 3485073)
SAP S/4HANA uses a third-party component SheetJS that contains a Regular Expression Denial of Service (ReDoS) vulnerability. An unauthenticated attacker could supply specially crafted input that triggers excessive processing within the affected functionality. Successful exploitation could exhaust system resources and make the service unavailable, resulting in a high impact on availability. There is no impact on confidentiality and integrity.
[CVE-2026-24316] Server-Side Request Forgery (SSRF) in SAP NetWeaver Application Server for ABAP (SAP Note 3689080)
SAP NetWeaver Application Server for ABAP provides an ABAP Report for testing purposes, which allows to send HTTP requests to arbitrary internal or external endpoints. The report is therefore vulnerable to Server-Side Request Forgery (SSRF). Successful exploitation could lead to interaction with potentially sensitive internal endpoints, resulting in a low impact on data confidentiality and integrity. There is no impact on availability of the application.
[CVE-2026-76975] Cross-Site Scripting (XSS) vulnerability in SAPUI5 (Support Assistant Overlay) (SAP Note 3794572)
Due to a DOM-Based Cross-Site Scripting (XSS) vulnerability, an unauthenticated attacker could generate a malicious link and make it publicly accessible. If an authenticated user accesses this link, client-side code reads the attacker-controlled input and writes it into the DOM without proper sanitization, causing attacker-supplied script to execute in the victim’s browser context. This could allow the attacker to access or modify information within the victim’s browser scope, impacting confidentiality and integrity, while availability remains unaffected.
[CVE-2026-0505] Multiple vulnerabilities in BSP Applications of SAP Document Management System (SAP Note 3678417)
This SAP Security Note addresses multiple vulnerabilities in Business Server Pages (BSP) applications of SAP Document Management System (DMS).
Open Redirect [CVE-2026-0505]
The BSP applications allow an unauthenticated user to manipulate user-controlled URL parameters that are not sufficiently validated. This could result in unvalidated redirection to attacker-controlled websites, leading to a low impact on confidentiality and integrity, and no impact on the availability of the application.
CVSS: 6.1; CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N
Cross-Site Scripting (XSS) [CVE-2026-24323]
The BSP applications allow an unauthenticated user to inject malicious script content via user-controlled URL parameters that are not sufficiently sanitized. When a victim accesses a crafted URL, the injected script is executed in the victim’s browser, leading to a low impact on confidentiality and integrity, and no impact on the availability of the application.
CVSS: 6.1; CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N
[CVE-2026-76976] Cross-Site Scripting (XSS) vulnerability in SAP NetWeaver Application Server ABAP (Applications based on SAP GUI for HTML) (SAP Note 3671819)
Applications based on SAP GUI for HTML in SAP NetWeaver Application Server ABAP do not sufficiently sanitize user-supplied content in certain functionality, allowing an authenticated attacker to send malicious content to another user. If the victim interacts with the affected content, malicious scripts could be executed in the victim’s browser context. This vulnerability has a low impact on the confidentiality and integrity of the data and no impact on the availability of the application.
[CVE-2026-89106] Cross Site Scripting (XSS) vulnerability in SAPUI5 (SAP Note 3799054)
SAP UI5 does not perform sufficient input validation under certain configurations. An attacker with low privileges could submit specially crafted content that is later rendered in a victim’s browser. This vulnerability has a low impact on confidentiality and integrity. There is no impact on availability.
About this Review
On the second Tuesday of each month, SAP release security updates to their software products. At Absoft, we analyse all the released security updates and produce this security review, including sending bespoke recommendations for each of our managed service customers.
There is more information on how we handle SAP security updates, including information on SAP’s process, the CVE process and the CVSS base scores in our earlier article on addressing security vulnerabilities in SAP software.