
Overview
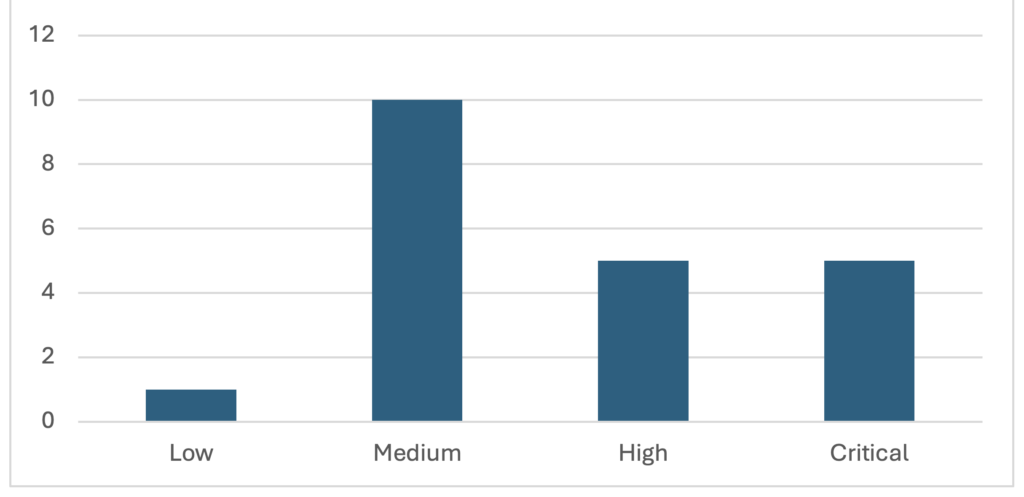
SAP’s security patch day for September 2026 has seen the release of 21 OSS SAP security notes. Five notes have been classified as critical, five as high, 10 as medium and one as low based on the CVSS v3.0 Rating.
Security Notes by CVSS v3 Base Score
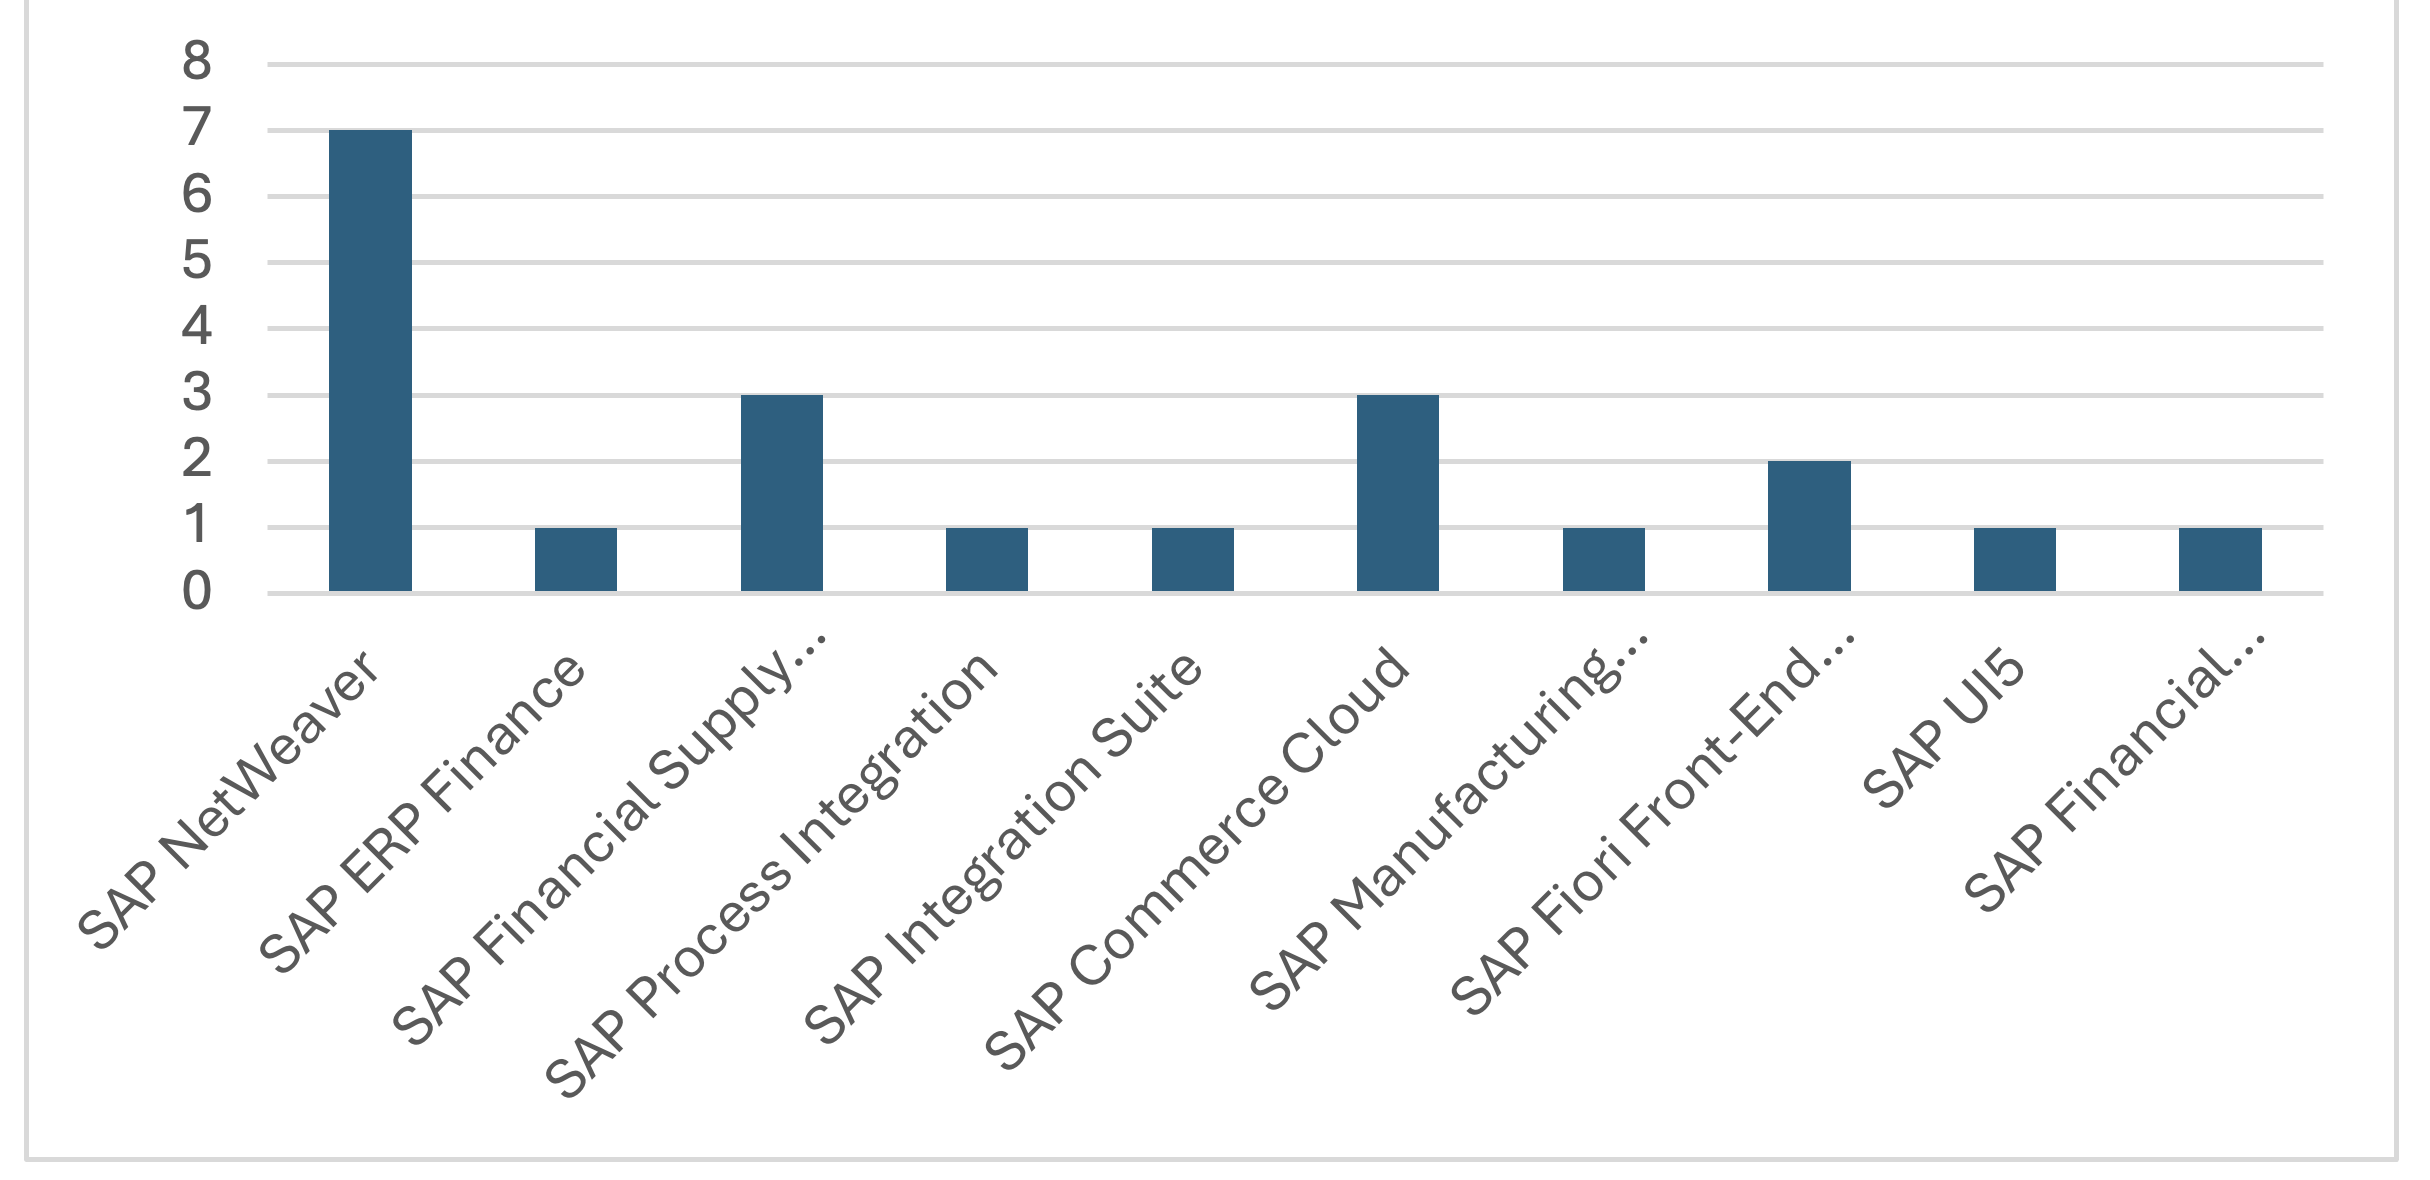
Seven notes have been released for:
- SAP NetWeaver
Three notes have been released for:
- SAP Financial Supply Chain Management
- SAP Commerce Cloud
Two notes have been released for:
- SAP Fiori Front-End Server
Single notes have been released for:
- SAP ERP Finance
- SAP Financial Consolidation
- SAP Integration Suite
- SAP Manufacturing Integration and Intelligence
- SAP Process Integration
- SAP UI5
Security Notes by Product Category
Vulnerabilities: September 2026 Highlights
[CVE-2026-44756] Memory Corruption vulnerability in SAP Extended Passport (EPP) Processing (SAP Note 3747649)
A memory safety vulnerability exists in the Extended Passport Protocol (EPP) processing library. Under specific conditions, an unauthenticated attacker could exploit a crafted network request containing a malformed EPP header, potentially resulting in undefined behavior and abnormal program termination. Successful exploitation may have a high impact on the confidentiality, integrity, and availability of the application.
[CVE-2026-58243] Privilege Escalation vulnerability in SAP ABAP Developer Tools (SAP Note 3772411)
SAP ABAP Development Tools does not perform necessary authorization checks for certain functionality, allowing an attacker with low privileges to execute unauthorized database operations against SAP NetWeaver AS ABAP. Successful exploitation could allow the attacker to read sensitive data, modify application data, and disrupt access for legitimate users, resulting in high impact on confidentiality, integrity, and availability.
[CVE-2026-66767] Memory Corruption vulnerability in SAP NetWeaver Application Server for ABAP and ABAP Platform (SAP Note 3757002)
SAP NetWeaver Application Server for ABAP and ABAP Platform allows an unauthenticated user to send a specially crafted packet that triggers reprocessing of a previously buffered user request, potentially hijacking another user’s session under narrow timing conditions. Successful exploitation could result in high impact on confidentiality and integrity, with low impact on availability of the application.
[CVE-2026-76968] Information Disclosure vulnerability in SAP Web Dispatcher, Internet Communication Manager and SAP Content Server (SAP Note 3750721)
SAP Web Dispatcher, Internet Communication Manager and SAP Content Server allows an authenticated low-privileged attacker to access certain administrative functionality or interface and obtain sensitive information about the system state, resulting in information disclosure. This disclosed information could potentially be used to facilitate further attacks. This vulnerability has a high impact on the confidentiality of the application, with no impact on integrity or availability.
[CVE-2026-44766] – SQL Injection vulnerability in SAP S/4HANA (Intercompany Matching and Reconciliation) (SAP Note 3756450)
SAP S/4HANA (Intercompany Matching and Reconciliation) allows a low-privileged authenticated user to inject malicious input into certain functions, which may be processed by the database without proper validation. This could allow the user to access sensitive information, resulting in high impact on confidentiality, with no impact on integrity and availability of the application.
[CVE-2026-76963] Missing Authorization Check in Application Server ABAP of SAP NetWeaver and ABAP Platform (SAP Note 3772838)
Due to a missing authorization check in Application Server ABAP of SAP NetWeaver and ABAP Platform, an authenticated attacker could gain unauthorized access to sensitive system configuration information. Successful exploitation could result in exposure of security relevant settings and internal system details, resulting in low impact on confidentiality while integrity and availability remain unaffected.
[CVE-2026-76977] Clickjacking vulnerability in SAPUI5(Frame Options Allowlist) (SAP Note 3783189)
SAP UI5 does not sufficiently validate the parent frame’s origin against the configured allowlist. An unauthenticated attacker could host a malicious page to bypass framing restrictions. If an authenticated victim visits the attacker’s page and interacts with it, the attacker could trick the victim into performing unintended actions, resulting in a low impact on integrity. There is no impact on confidentiality and availability.
[CVE-2026-76962] Missing Authorization check in SAP S/4HANA (Manage Bank Chains app) (SAP Note 3657599)
SAP S/4HANA (Manage Bank Chains app) does not perform sufficient authorization checks within certain affected functionality. An attacker with low privileges could send specially crafted requests to delete specific entries that should not be accessible to them. This results in a low impact on availability. There is no impact on confidentiality and integrity.
About this Review
On the second Tuesday of each month, SAP release security updates to their software products. At Absoft, we analyse all the released security updates and produce this security review, including sending bespoke recommendations for each of our managed service customers.
There is more information on how we handle SAP security updates, including information on SAP’s process, the CVE process and the CVSS base scores in our earlier article on addressing security vulnerabilities in SAP software.