
Overview
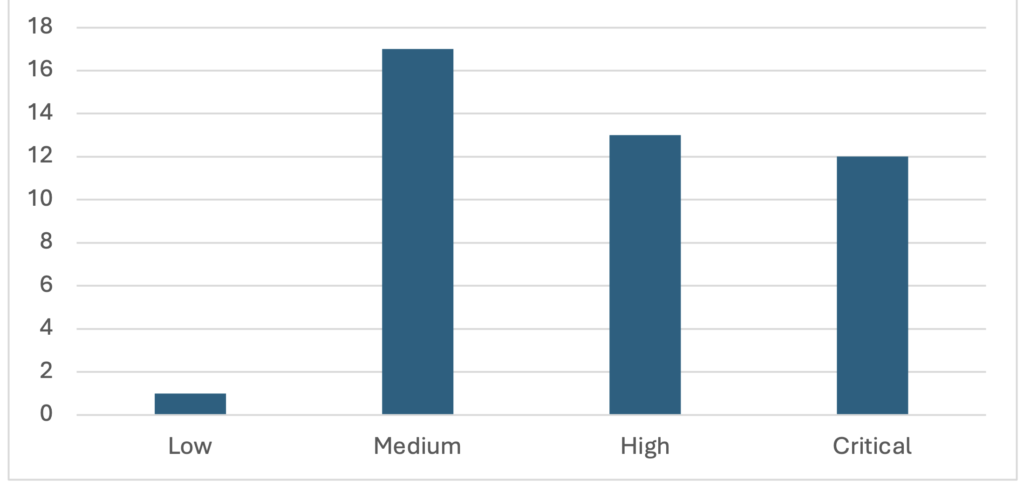
SAP’s security patch day for November 2026 has seen the release of 43 OSS SAP security notes. 12 notes have been classified as critical, 13 as high, 17 as medium and one as low based on the CVSS v3.0 Rating.
Security Notes by CVSS v3 Base Score
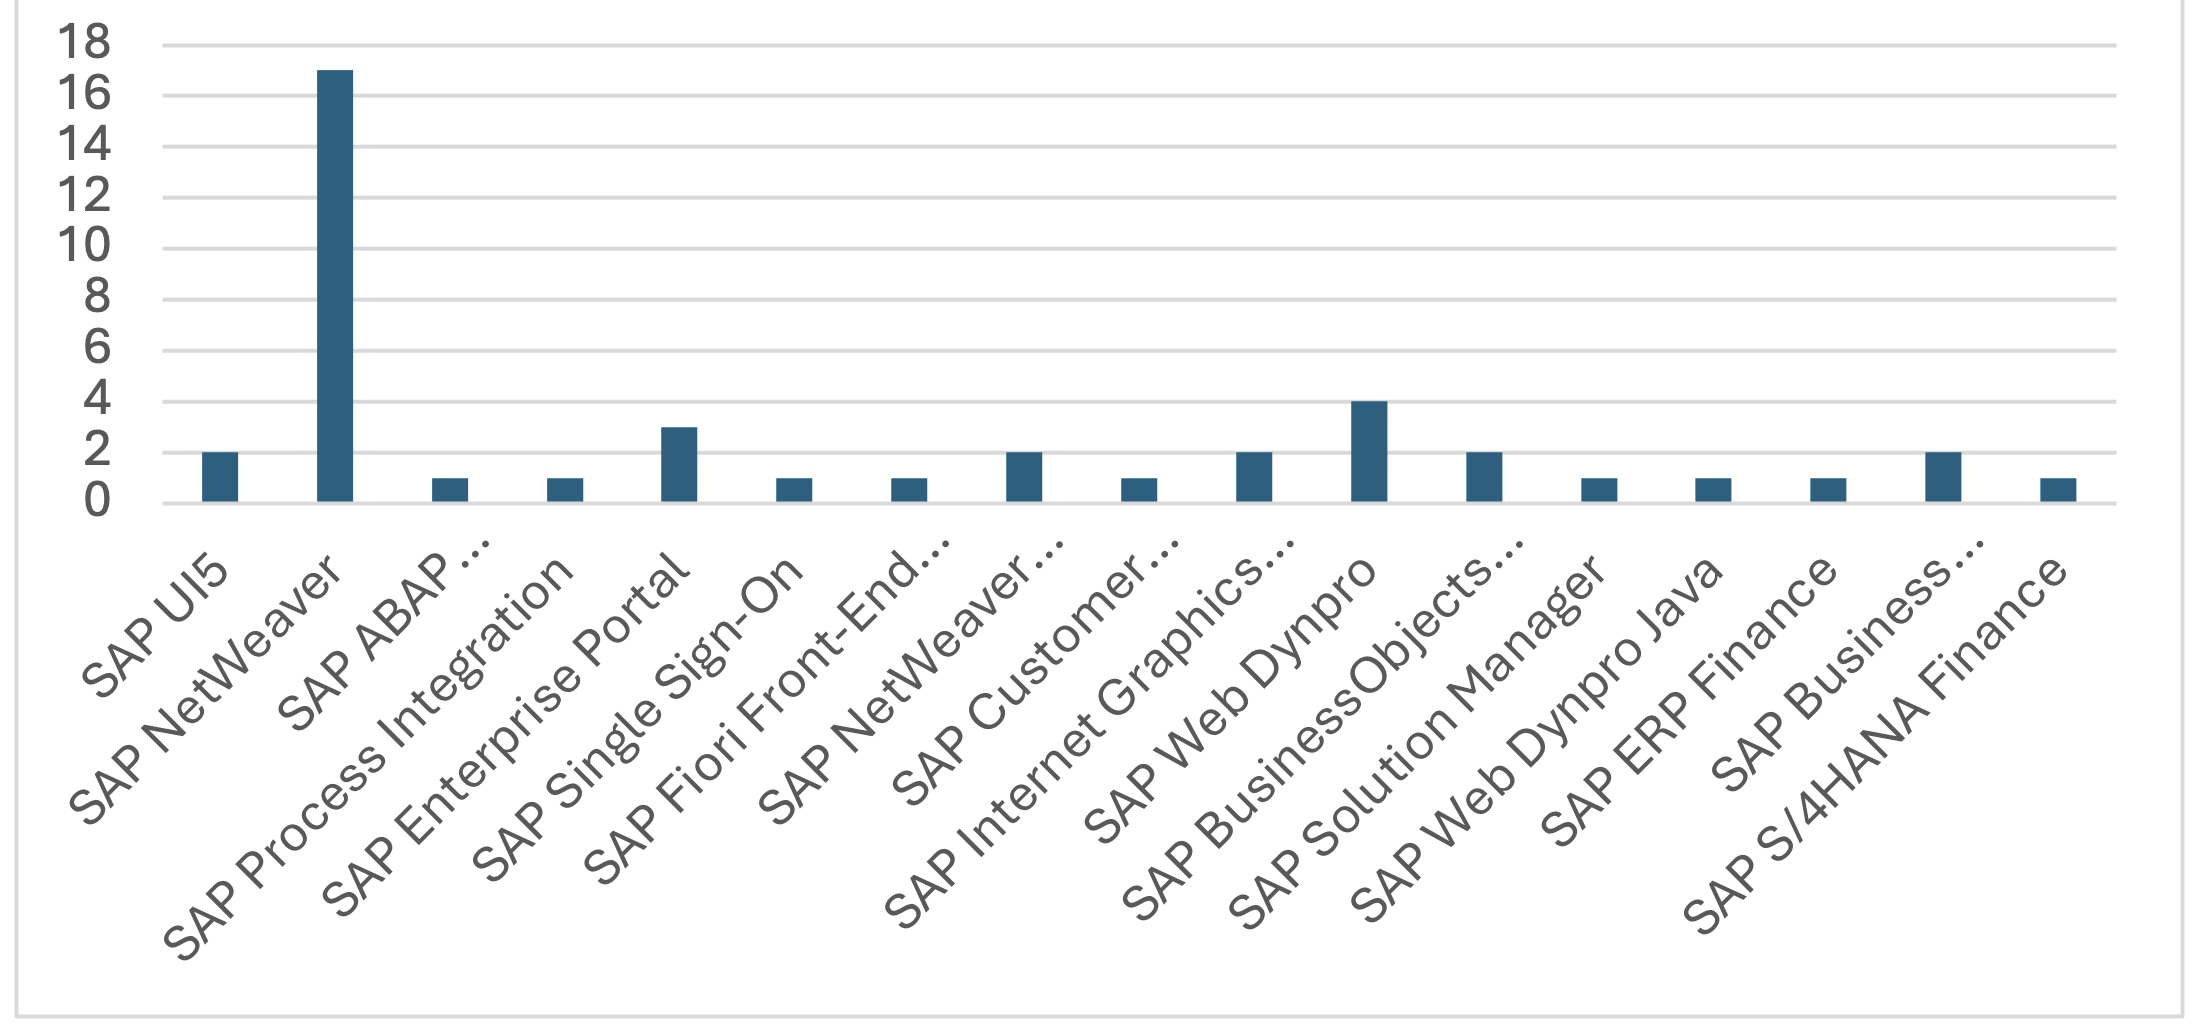
Seventeen notes have been released for:
- SAP NetWeaver
Four notes have been released for:
- SAP Web Dynpro
Three notes have been released for:
- SAP Enterprise Portal
Two notes have been released for:
- SAP UI5
- SAP NetWeaver Application Server Java
- SAP Internet Graphics Server
- SAP BusinessObjects Business Intelligence
- SAP Business Technology Platform
Single notes have been released for:
- SAP ABAP Development Tools
- SAP Process Integration
- SAP Single Sign-On
- SAP Fiori Front-End Server
- SAP Customer Relationship Management
- SAP Solution Manager
- SAP Web Dynpro Java
- SAP ERP Finance
- SAP S/4HANA Finance
Security Notes by Product Category
Vulnerabilities: November 2026 Highlights
[CVE-2026-120017] Missing Authentication in SAP NetWeaver AS ABAP and ABAP Platform (SAML2 Service Provider) (SAP Note 3849308)
SAP NetWeaver AS ABAP and ABAP Platform does not perform sufficient verification of incoming authentication assertions under certain configurations. An unauthenticated attacker could submit specially crafted data to bypass authentication and impersonate arbitrary users, including privileged accounts. Successful exploitation could cause a full system compromise, with the impact potentially extending to connected components and systems beyond the affected system. This results in a high impact on confidentiality, integrity, and availability of the application.
[CVE-2026-89103] Broken Access Control in SAP Gateway (SAP Note 3798345)
SAP Gateway activates the default Access Control List with high privileges allowing categorization of external attacker as internal application server. As a result an unauthenticated attacker with network access to the SAP Gateway could exploit this weakness to potentially perform unauthorized actions within the application environment, resulting in a high impact on the confidentiality, integrity, and availability of the affected system.
[CVE-2026-89126] Memory Corruption vulnerability in SAP Web Dispatcher (SAP Note 3778556)
SAP Web Dispatcher does not sufficiently validate certain network input processed by an internal component. An unauthenticated attacker could send specially crafted network traffic to trigger a memory corruption condition in the affected functionality. Successful exploitation could allow the attacker to execute arbitrary code and fully compromise the system, resulting in a high impact on confidentiality, integrity and availability of the system.
[CVE-2026-76964] Memory Corruption Vulnerability in SAP NetWeaver AS ABAP (Internet Communication Manager) (SAP Note 3778530)
SAP NetWeaver Application Server ABAP does not sufficiently validate certain network input processed by an internal component. An unauthenticated attacker could send specially crafted network traffic to trigger a memory corruption condition in the affected functionality. Successful exploitation could allow the attacker to execute arbitrary code and fully compromise the system, resulting in a high impact on confidentiality, integrity and availability of the system.
[CVE-2026-109795] Missing authorization check in S4CRM (SAP Note 3834842)
SAP NetWeaver does not perform necessary authorization checks and lacks sufficient input validation in certain remote-enabled functionality. An attacker with low privileges could send specially crafted input through a remote interface to inject and execute arbitrary code within the affected system. Successful exploitation could extend the attacker’s reach beyond the vulnerable component, resulting in a high impact on confidentiality, integrity and availability.
[CVE-2026-76965] OS Command Injection vulnerability in ABAP Application Server for SAP NetWeaver and ABAP Platform (SAP Note 3792735)
SAP NetWeaver Application Server ABAP and ABAP Platform does not perform necessary authorization checks for certain internal functionality. An attacker with low privileges could invoke affected functionality to execute arbitrary operating system commands on the underlying host. Successful exploitation could impact resources beyond the vulnerable component, resulting in a high impact on confidentiality, integrity and availability of the system.
[CVE-2026-89107] Code Injection vulnerability in SAP S/4HANA (Manage Substitution/Validation Rules) (SAP Note 3805589)
SAP S/4HANA (Manage Substitution/Validation Rules) does not sufficiently validate input processed by rule definition functionality that utilizes a domain-specific scripting language. An authenticated attacker with specific business privileges could submit specially crafted input, which is interpreted as executable ABAP code by the rule processing logic. Successful exploitation could allow the attacker to execute ABAP arbitrary code into the system, resulting in full compromise of the affected system and high impact on confidentiality, integrity, and availability of the system.
[CVE-2026-89119] Cross-Site Request Forgery (CSRF) vulnerability in SAP Web Dispatcher and Internet Communication Manager (SAP Note 3804858)
This SAP security note addresses several vulnerabilities identified in SAP Web Dispatcher and Internet Communication Manager. The vulnerability details along with their CVE relevant information can be found below.
Cross-Site Request Forgery (CSRF) vulnerability in SAP Web Dispatcher and Internet Communication Manager [CVE-2026-89119]: SAP Web Dispatcher and SAP NetWeaver Application Server ABAP (Internet Communication Manager) do not perform sufficient request validation in certain administrative functionality. In the context of Application Server ABAP and SAP Web Dispatcher, an unauthenticated attacker could trick a logged-on administrator into visiting a malicious link. Visiting the link could cause unintended actions in the administrator’s session. Successful exploitation could lead to a full compromise of the underlying operating system, resulting in a high impact on confidentiality, integrity, and availability.
CVSS: 9.6; CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:H
Cross-Site Request Forgery (CSRF) vulnerability in SAP HANA XSA Web Dispatcher [CVE-2026-120014]: SAP HANA XSA Web Dispatcher does not perform sufficient request validation in certain administrative functionality. In the context of SAP HANA XSA Web Dispatcher, an unauthenticated attacker could trick a logged-on administrator into visiting a malicious link. Visiting the link could cause unintended actions in the administrator’s session. Successful exploitation could lead to a temporary compromise of the SAP HANA XSA Web Dispatcher, resulting in a high impact on confidentiality, and partial impact on integrity, and availability.
CVSS: 7.6; CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:L/A:L
About this Review
On the second Tuesday of each month, SAP release security updates to their software products. At Absoft, we analyse all the released security updates and produce this security review, including sending bespoke recommendations for each of our managed service customers.
There is more information on how we handle SAP security updates, including information on SAP’s process, the CVE process and the CVSS base scores in our earlier article on addressing security vulnerabilities in SAP software.